Solutions · Technology & SaaS
Answer auditors and customers from the same live checks.
Software companies get asked for proof by their auditors and by every enterprise customer's security review. Venevor reads the systems you build and run on and keeps that proof current.
- SOC 2readiness report
- 1 checkmany frameworks
- CitedAsk Venevor answers
1Connectors
Read the systems you already build and run on.
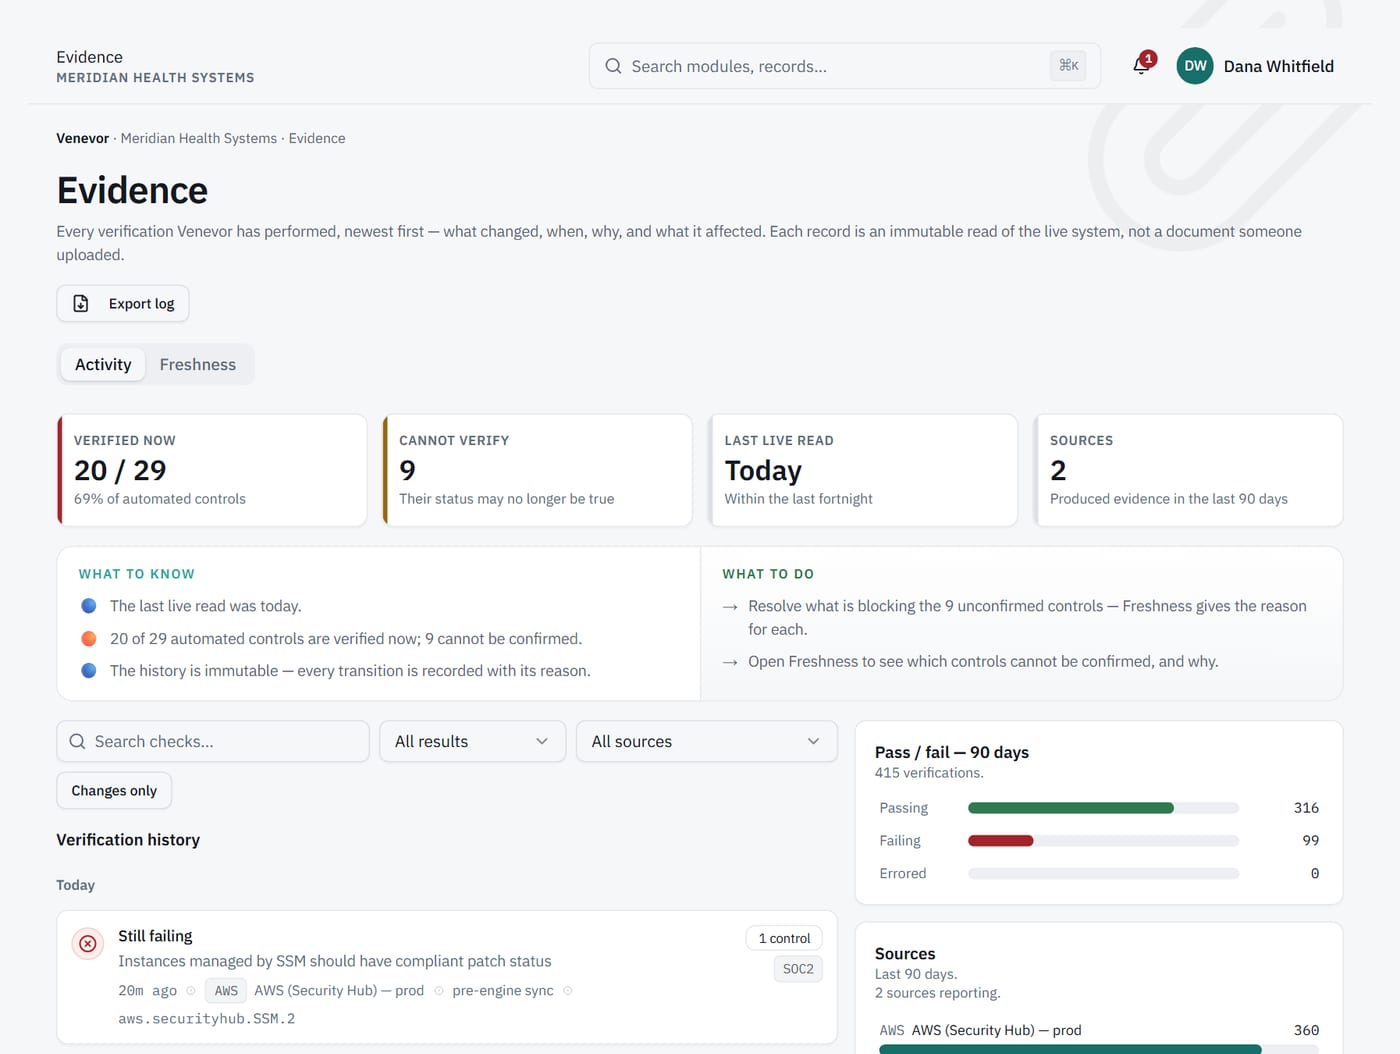
Checks read AWS (including Security Hub), GitHub, Okta and Jira directly. Each result names the system it read, what it found and when.
What it does
Map one check to SOC 2, ISO 27001 and other frameworks.
What it never does
Record an unreadable source as a pass.
2Audits
Give auditors a dedicated workspace with live evidence.
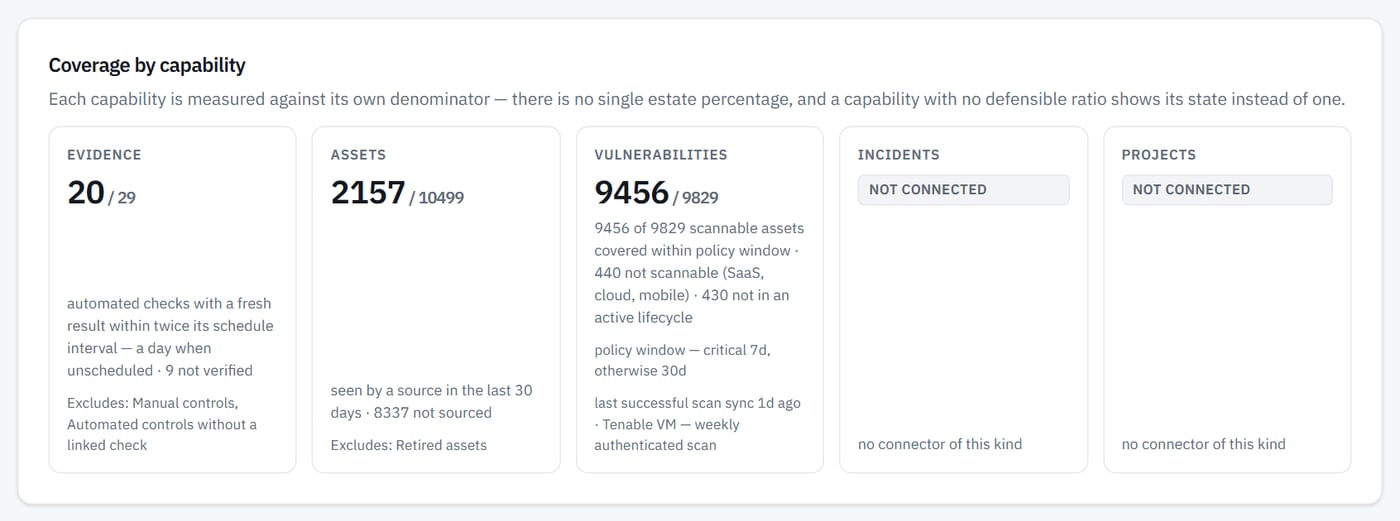
Auditors get access to controls and evidence, with freshness shown on every item. They export findings and a live evidence package themselves.
3Customer reviews
Answer security questions with cited, current facts.
Ask Venevor is an assistant that answers from your own records and cites where each answer came from. The in-app Trust Center gives your team a live view of control status.
Capabilities
What's included.
SOC 2 readiness report
A built-in report shows SOC 2 readiness across the five states, with the evidence behind each.
Policies with e-signature
Policies are approved with e-signature and acknowledged by the people they apply to.
Jira project sync
Projects sync with Jira and carry risk signals, so security work is tracked where engineers already work.
Fix-first vulnerability queue
Findings are prioritized with CISA KEV and EPSS, so known-exploited issues come first.
Exceptions with an expiry
An accepted gap carries a named owner and an expiry date, so it comes back for review.
API keys with usage
API keys carry usage tracking, so you can see how each key is used.
Works with
Connected to the rest of Venevor.
FAQ
Common questions.
Does Venevor replace our SOC 2 auditor?
No. Your auditor still issues the report. Venevor prepares the evidence and gives the auditor a dedicated workspace to review it.
Can our customers see our Trust Center?
The Trust Center is a live view inside Venevor for your own team. Share what you choose with customers through reports and exports.
Can Ask Venevor change our records?
No. Ask Venevor never changes your records. It answers from your organization's records and cites the source of each answer.
See SOC 2 readiness on synthetic data.
We'll walk through checks, audits and Ask Venevor on data shaped like a software company's.