Solutions · Enterprise
Proof at enterprise scale.
Roll exposure up by business entity, put a dollar range on risk for the board, and control who sees what with custom roles, single sign-on and SCIM, all on one body of evidence.
- 0–1,000
- Exposure Score by entity
- FAIR
- aligned financial risk
- SCIM 2.0
- user and group provisioning
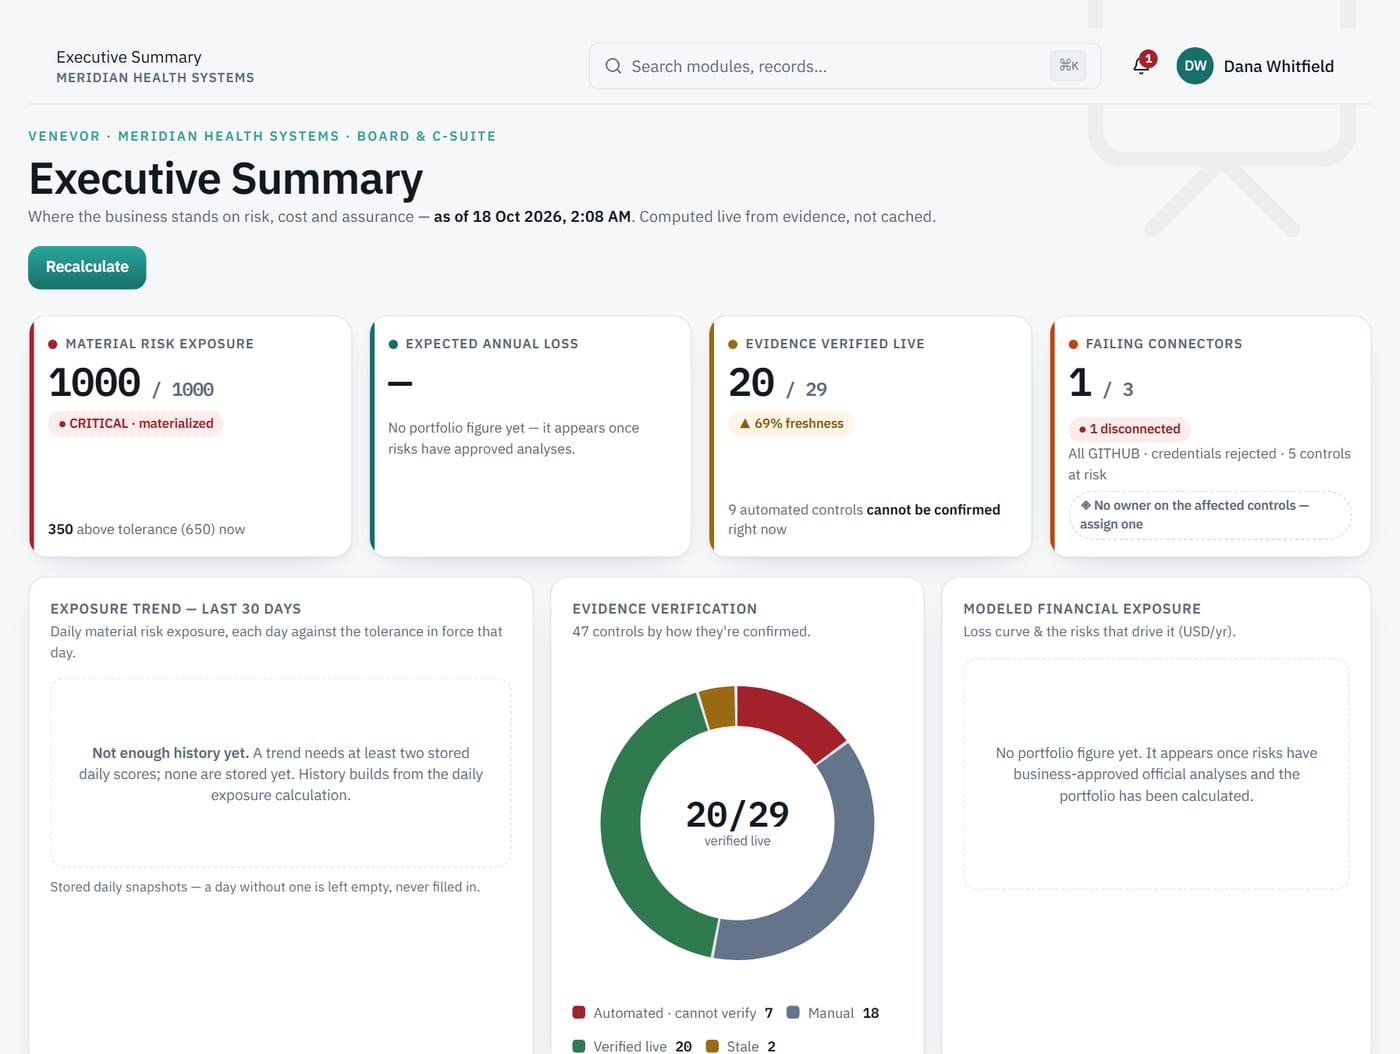
1Business entities
See exposure for every part of the business.
Define your subsidiaries, business units or brands as business entities and assign assets to them. The Exposure Score rolls up per entity and for the whole organization, with a daily history.
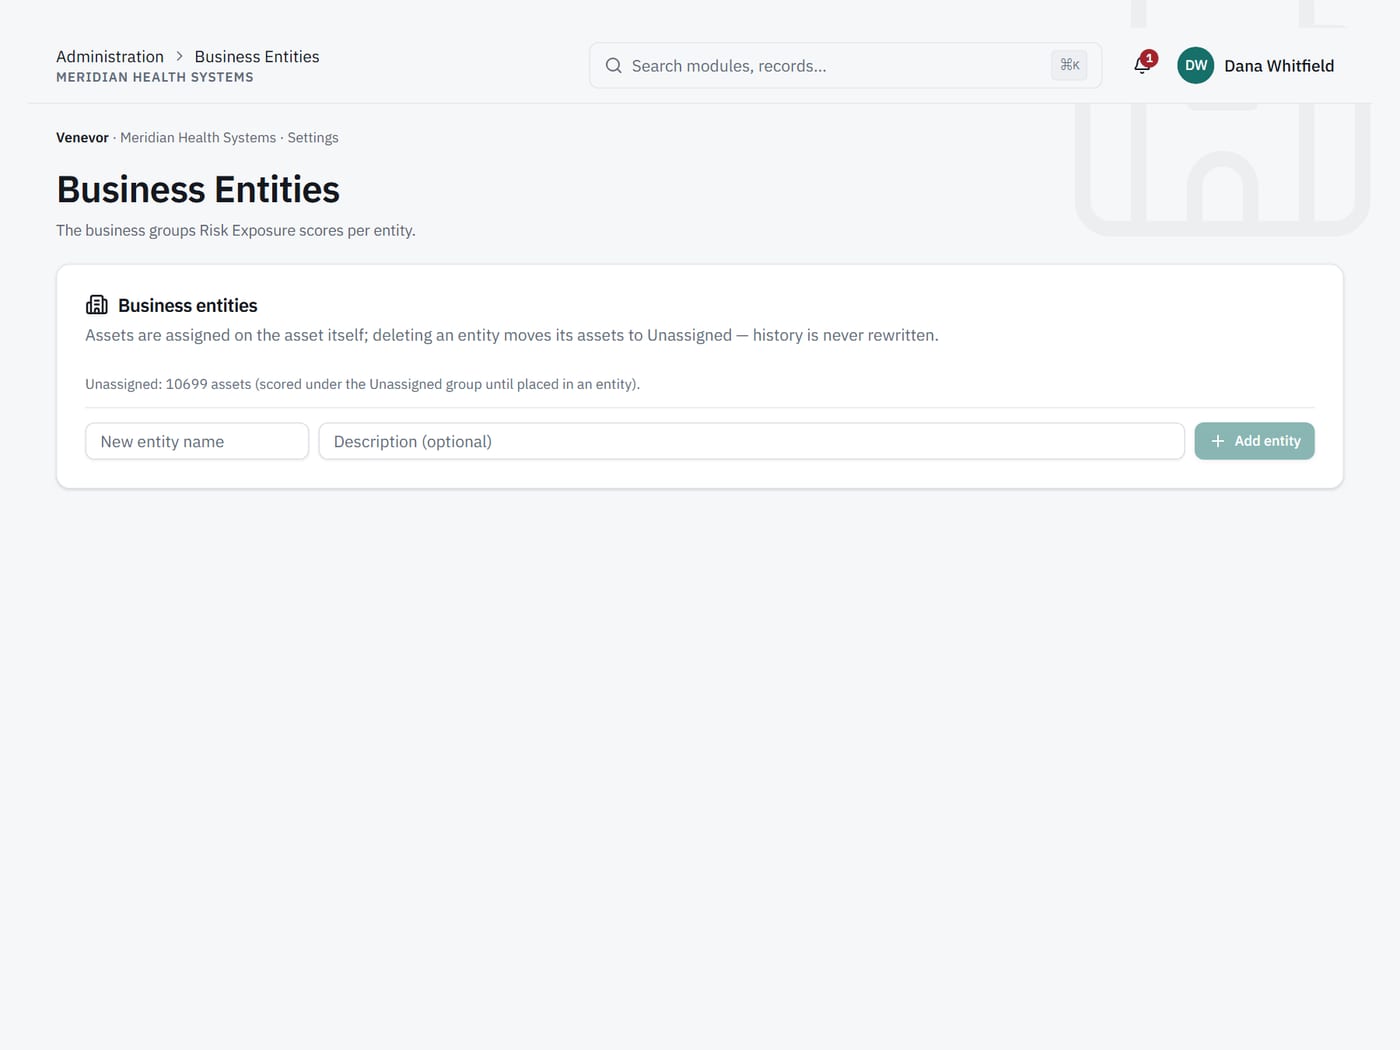
2Board-level risk
Put a dollar range on the risks that matter.
FAIR-aligned Monte Carlo runs are seeded and reproducible, assumptions are approved before they count, and treatments are compared on the loss they remove. The board report draws on the same numbers.
What it does
Shows the method behind every number.
What it never does
Present a single number as a certainty.
3Access and data
Access and data controls your security team expects.
OIDC single sign-on with group-to-role mapping, mandatory MFA, SCIM provisioning and custom roles built from the same permissions. Every sensitive action is written to an audit log nobody can edit.
Capabilities
What's included.
Business-entity rollups
Exposure per subsidiary, business unit or brand.
Financial risk
Reproducible FAIR-aligned runs and a portfolio view.
Custom roles
Granular permissions by module and action.
SCIM provisioning
Users and groups provisioned from your identity provider.
Immutable audit log
Sign-ins, exports and permission changes are written to a log nobody can edit.
OSCAL and FedRAMP exports
OSCAL assessment results and SSP and POA&M foundation exports.
Works with
Connected to the rest of Venevor.
FAQ
Common questions.
Can we see risk by subsidiary or business unit?
Yes. Define business entities, assign assets to them, and the Exposure Score rolls up per entity and for the whole organization.
Does Venevor work with our identity provider?
Yes. Venevor supports OIDC single sign-on with group-to-role mapping and SCIM 2.0 user and group provisioning. MFA is mandatory.
How is our data kept apart from other customers'?
Every record carries your organization's identifier, and the database itself refuses to return another organization's rows.
Bring your security team to the demo.
We'll cover entities, risk, access and data handling for an organization your size.