Solutions · Startups
Your first audit, ready from day one.
Connect AWS, Okta and GitHub, pick your first framework, and see which requirements your systems already prove. No spreadsheet to build, no compliance team required.
- 1 check
- counts toward many frameworks
- SOC 2
- readiness report built in
- 5
- readiness states
1Get started
Start from the systems you already run.
Connect your cloud, identity provider and code repositories. Automated checks read them on a schedule, and each result maps to every framework it supports, so the first framework does most of the work for the next one.
What it does
Shows which requirements your systems already prove.
What it never does
Count a box someone ticked as verified.
2Policies
Policies approved, signed and acknowledged.
Write or import your security policies, approve them with an electronic signature, and collect acknowledgements from the team. Export them branded as PDF or Word when a customer asks.
3Your first audit
Hand your auditor the evidence, not a folder.
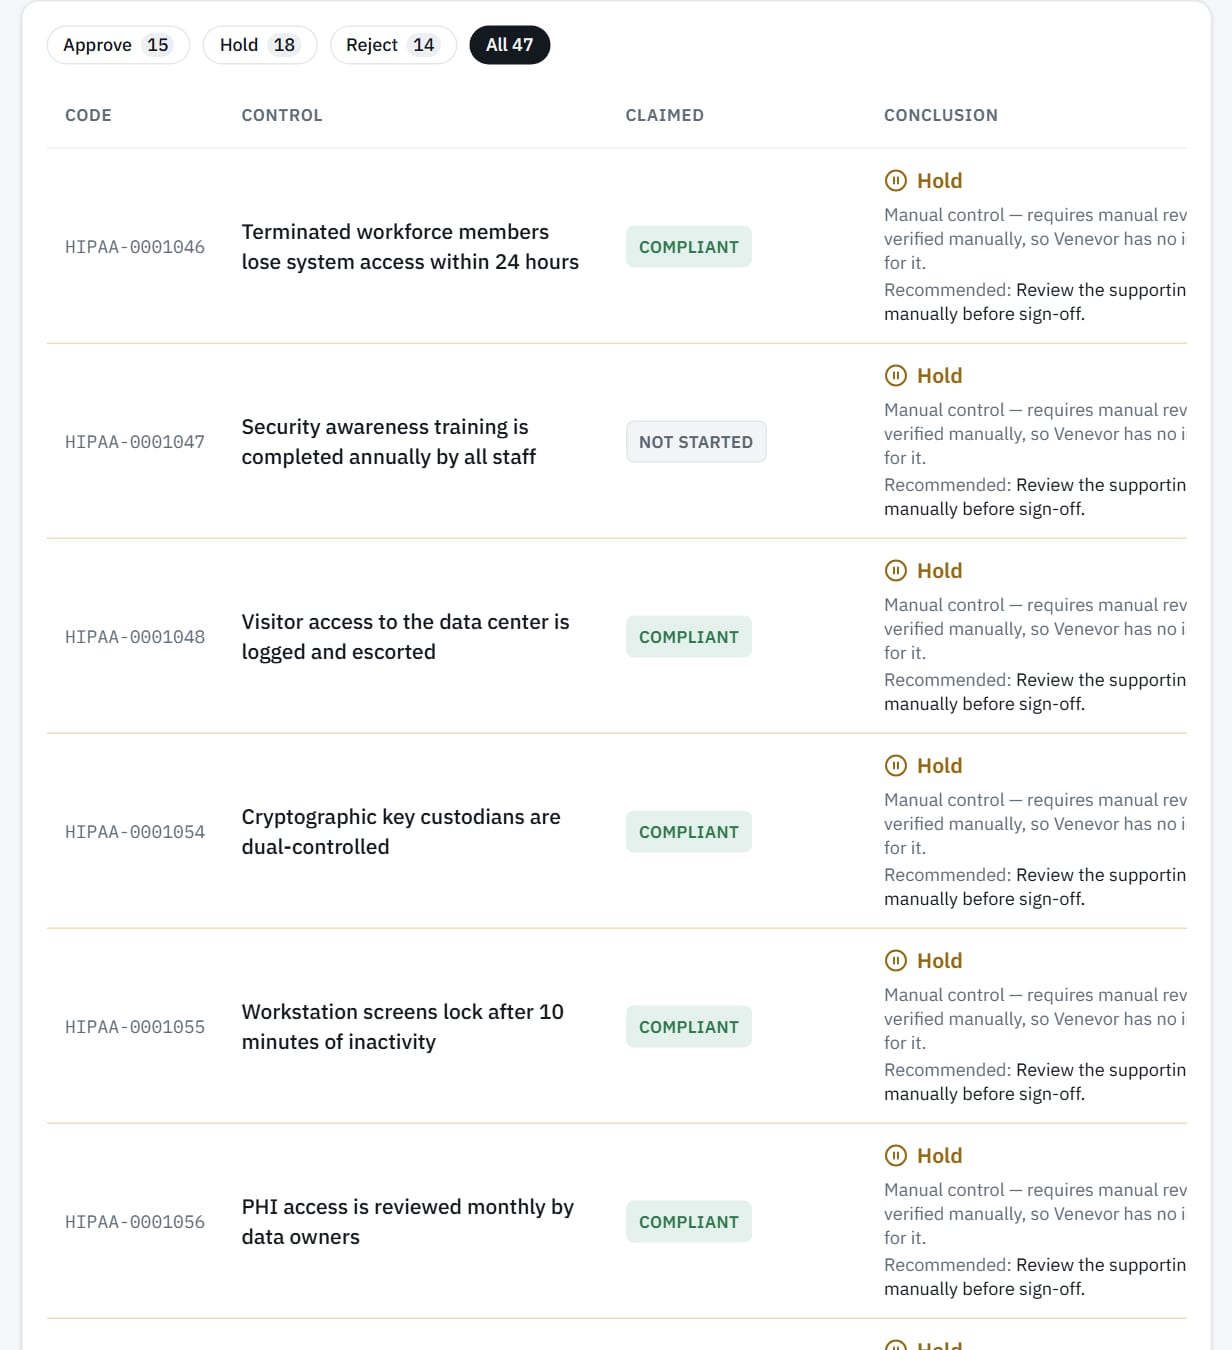
Your auditor gets a dedicated workspace with each claim beside its evidence and a live evidence package to export. The SOC 2 readiness report shows where you stand before they arrive.
Capabilities
What's included.
Connect your stack
AWS, Okta, GitHub and Jira connect without changing your systems.
Ready-made controls
Start from Venevor's library of 77 controls instead of a blank page.
SOC 2 readiness report
See readiness per requirement, verified apart from asserted.
Policy approval
E-signature approval and team acknowledgement in one place.
Vendor questionnaires
Send scored questionnaires to the vendors your customers ask about.
Room to grow
Add HIPAA, ISO 27001 or more frameworks on the same evidence.
Works with
Connected to the rest of Venevor.
FAQ
Common questions.
We have no compliance team. Can we still use Venevor?
Yes. Connect your systems, pick a framework and work through the gaps Venevor shows you. The readiness view tells you what to do next.
Which framework should we start with?
Usually the one your customers ask for, which for many software companies is SOC 2. Because checks map to several frameworks, the evidence you collect also counts toward the next one.
Does Venevor replace our auditor?
No. Your auditor still issues the report. Venevor prepares the evidence and gives the auditor a dedicated workspace to review it.
Walk into your first audit prepared.
A walkthrough on the systems you already run, built around the framework your customers ask for.