Frameworks · Security
MVSP
Venevor tracks MVSP controls for your own product and helps you hold vendors to the same baseline through questionnaires.
- Issued byMVSP working group
- Applies toB2B software and service providers
One check
Counts toward
- MVSPVerified
- SOC 2Verified
- ISO 27001Verified
The framework
What MVSP asks of you.
What it is
MVSP is a minimum security baseline for business-to-business software and business process outsourcing suppliers, developed by a working group of industry practitioners. It is a short checklist of controls grouped into business, application design, application implementation and operational areas. Buyers use it in procurement and vendor reviews, and suppliers use it to show a baseline before more detailed assessments.
Minimum Viable Secure Product
Who needs it
- SaaS companies answering security reviews
- Procurement and third-party risk teams
- Early-stage companies building a baseline before SOC 2 or ISO 27001
1Your product
Track the baseline for what you ship
Each MVSP control shows its readiness and evidence. Connectors such as GitHub and AWS read the systems behind many of the technical controls.
2Your vendors
Hold suppliers to the same baseline
Send vendor questionnaires and keep each response with the vendor's record. Third-party risk sits beside your own controls.
3Next step
A foundation for SOC 2 and ISO 27001
Many MVSP controls overlap with SOC 2 and ISO 27001. One check maps to every framework it supports, so the work carries forward.
What it does
Shows where MVSP shares controls with your other frameworks.
What it never does
Count a control as verified because someone said so.
Capabilities
Built for MVSP.
MVSP pack
Business, design, implementation and operational controls, mapped to your controls.
Vendor questionnaires
Send questionnaires to vendors and keep their responses with the vendor's record.
Code and cloud evidence
GitHub and AWS connectors supply evidence for technical controls.
Framework overlap view
See where MVSP shares controls with SOC 2 and ISO 27001.
Policy approvals
Policies are approved with e-signature and acknowledged by staff.
Five readiness states
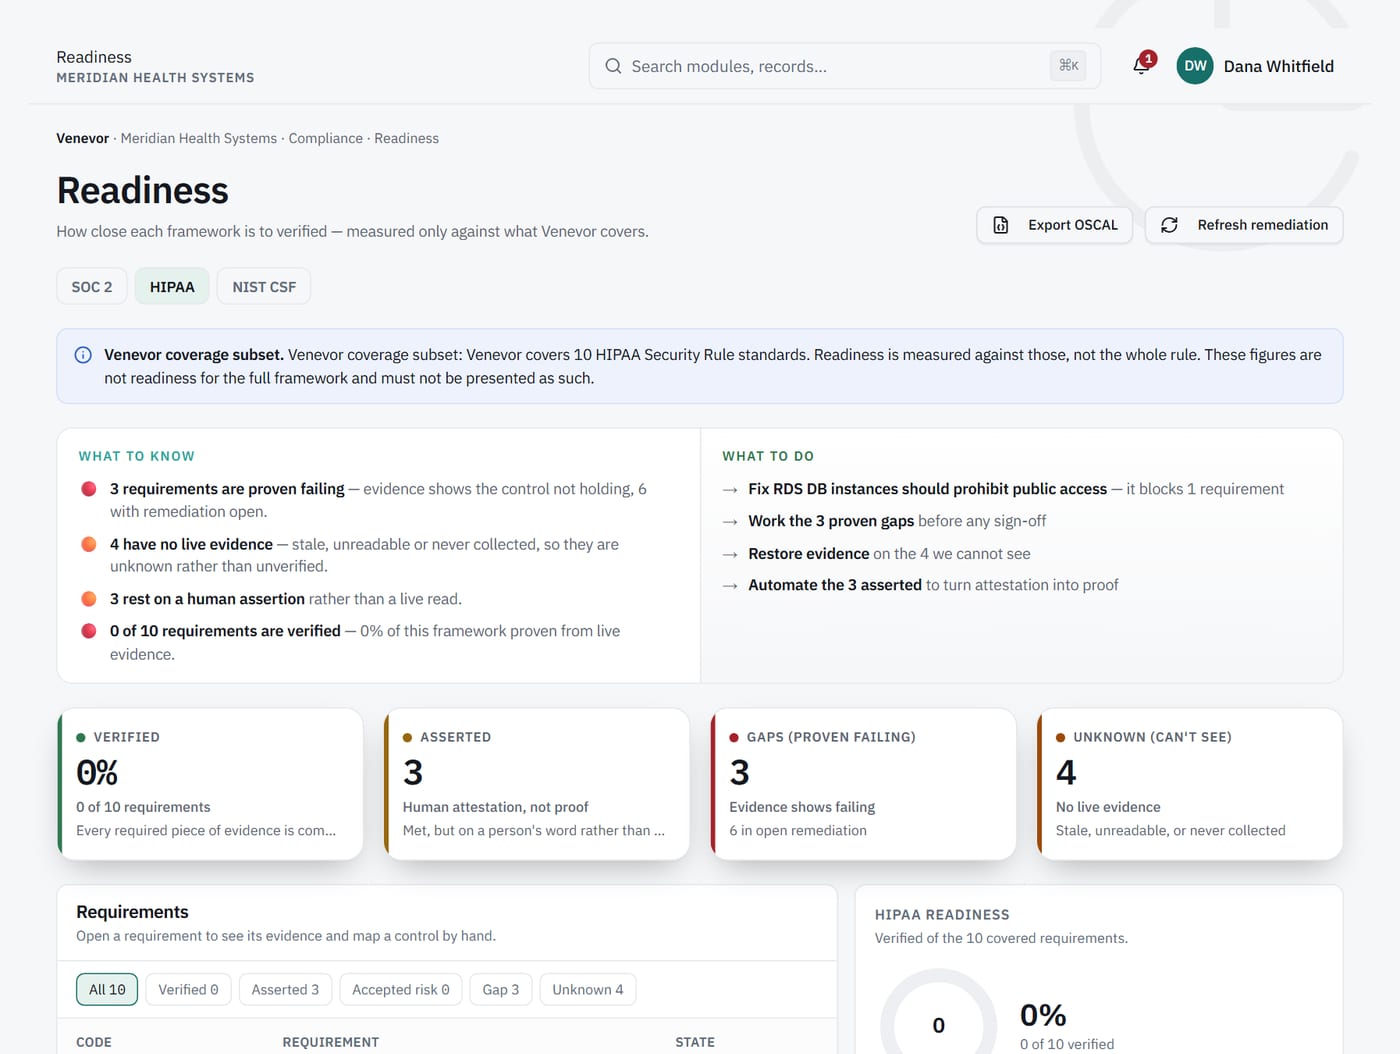
Verified, Asserted, Exception, Gap and Unknown, with verified and asserted never added together.
One set of evidence
The same checks count toward other frameworks.
- Security
SOC 2
Prepare Common Criteria evidence for your SOC 2 audit.
See SOC 2 → - Security
ISO 27001
Prepare your ISMS and Annex A controls for certification.
See ISO 27001 → - Compliance
Compliance automation
Controls that prove themselves from live checks.
Learn more → - Operations
Third-party risk
Vendor questionnaires, portal and approval routing.
Learn more → - Compliance
Evidence
Every check result, timestamped and kept.
Learn more →
FAQ
MVSP questions.
Is MVSP a certification?
No. MVSP is a self-assessed checklist with no certifying body. Venevor helps you track your answers and the evidence behind them.
Can we use MVSP to assess our vendors?
Yes. Send vendor questionnaires built around the baseline and keep each response with the vendor's record.
Should we do MVSP or SOC 2?
They serve different purposes. MVSP is a short baseline, and SOC 2 is an independent audit report many customers require. Venevor tracks both, and shared controls are checked once.
Which connectors help with MVSP?
GitHub and AWS cover much of the code and infrastructure side, and Okta or Microsoft Entra ID cover identity.
See your MVSP readiness on real evidence.
A walkthrough built around your frameworks and the systems you already run.