Solutions · Healthcare
Show which HIPAA safeguards your evidence supports today.
Healthcare organizations answer to regulators, patients and partners. Venevor reads your identity, cloud and endpoint systems, maps each result to HIPAA safeguards, and shows which ones current evidence supports and which still rest on someone's word.
- HIPAA
- safeguards mapped
- 5
- readiness states
- Live
- evidence package per audit
1Readiness
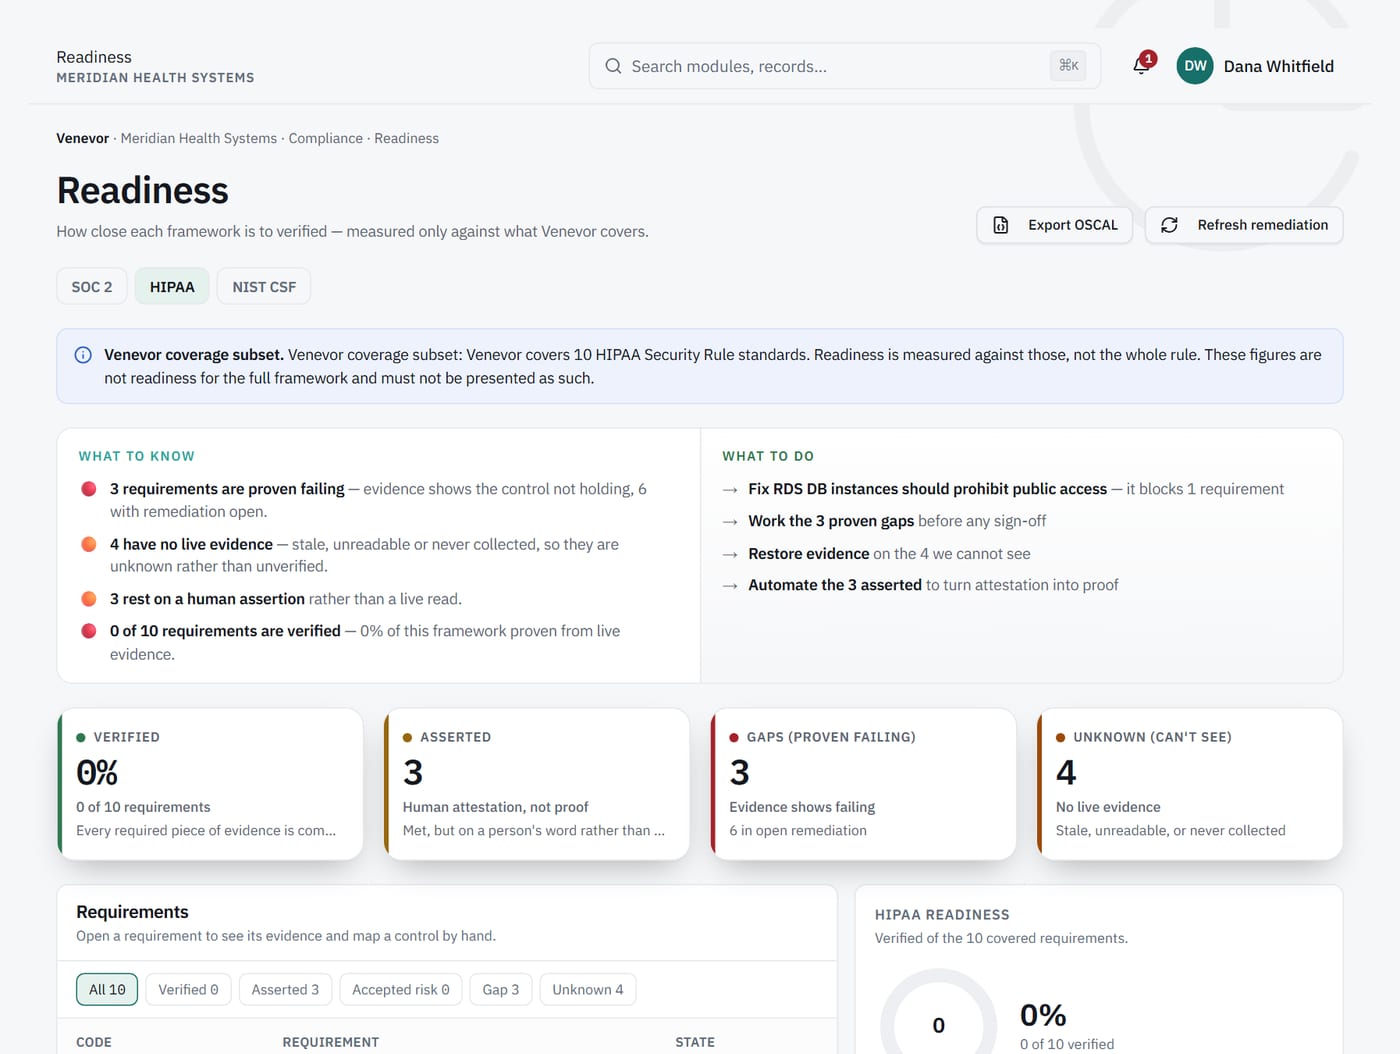
Know which safeguards are verified and which are asserted.
Each safeguard shows one of five states: Verified, Asserted, Exception, Gap or Unknown. Automated controls take their status from the latest check, so a passing result is a current reading of the system. When a source can't be read, the check records an error.
What it does
Map one check to HIPAA and every other framework that asks for it.
What it never does
Let anyone set an automated control to passing by hand.
2Incidents
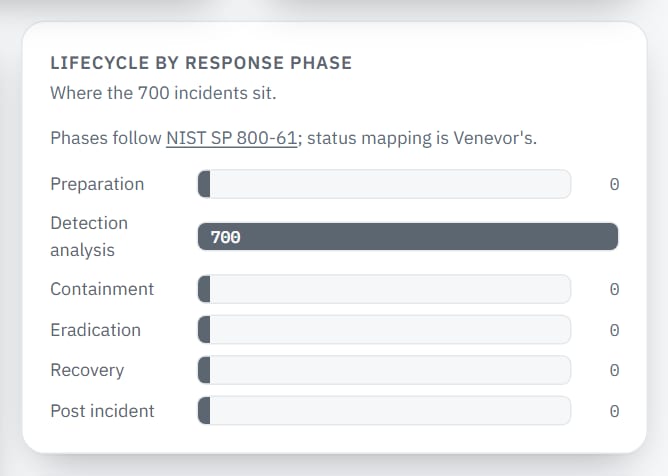
Track incidents by phase, with notification status recorded.
Incidents move through defined phases with an owner. Breach-notification status sits on the incident record, so the team can see where notification stands without a separate tracker.
3Third parties
Assess the vendors that handle your data.
Vendors answer scored questionnaires in their own portal, and approval routes to the people your policy names. Reassessments come due so a vendor approved last year is looked at again.
Capabilities
What's included.
Mapped HIPAA safeguards
Controls map to HIPAA safeguards, and one check can count toward many frameworks at once.
Evidence that keeps its date
Every piece of evidence is timestamped, kept and never edited, with its freshness shown.
Policy approval and acknowledgement
Policies are approved with e-signature and acknowledged by the people they apply to.
Exceptions with an expiry
An accepted gap carries a named owner and an expiry date, so it comes back for review.
Identity and endpoint connectors
Venevor reads Okta, Microsoft Entra ID, Intune, Defender, CrowdStrike and AWS.
Immutable audit log
Sign-ins, exports and permission changes are written to a log nobody can edit.
Works with
Connected to the rest of Venevor.
FAQ
Common questions.
Does using Venevor mean we meet HIPAA?
Not on its own, and no software can promise that. Venevor maps your controls to HIPAA safeguards, gathers evidence from your systems, and shows which safeguards current evidence supports and where the gaps are.
Which systems can it read?
Built connectors include AWS, Okta, GitHub, Microsoft Entra ID, Intune, Defender, CrowdStrike, Tenable, Qualys, ServiceNow and Jira. Each automated result names the system it read and when.
How is our data kept apart from other organizations?
The database enforces row-level isolation for every organization, and the audit log refuses edits and deletes. The Trust page explains both in more detail.
See your safeguards on synthetic data.
We'll walk through readiness, evidence and incidents on data shaped like a healthcare organization's.