Frameworks · Government
NIST SP 800-171
Venevor tracks NIST SP 800-171 under either revision, checks the controls it can read from your systems, and shares that evidence with CMMC Level 2.
- Issued byNIST
- Applies toNonfederal organizations handling CUI
One check
Counts toward
- NIST SP 800-171Verified
- CMMCVerified
- NIST CSF 2.0Verified
The framework
What NIST SP 800-171 asks of you.
What it is
NIST SP 800-171 sets security requirements for protecting Controlled Unclassified Information (CUI) in nonfederal systems. Federal contracts, including DoD contracts that carry DFARS 252.204-7012, require contractors to implement it. Revision 3, published in 2024, restructured the requirements to align more closely with NIST SP 800-53 and introduced organization-defined parameters.
NIST Special Publication 800-171, Protecting Controlled Unclassified Information in Nonfederal Systems and Organizations
Who needs it
- Defense contractors and subcontractors
- Universities and research institutions with federal contracts involving CUI
- Manufacturers and service providers in federal supply chains
1Two revisions
Rev. 2 and Rev. 3, side by side
Venevor has packs for both revisions. Work to the one your contracts reference today, and use the overlap view to see how your controls carry into the other.
2Requirement families
Every family tracked with its evidence
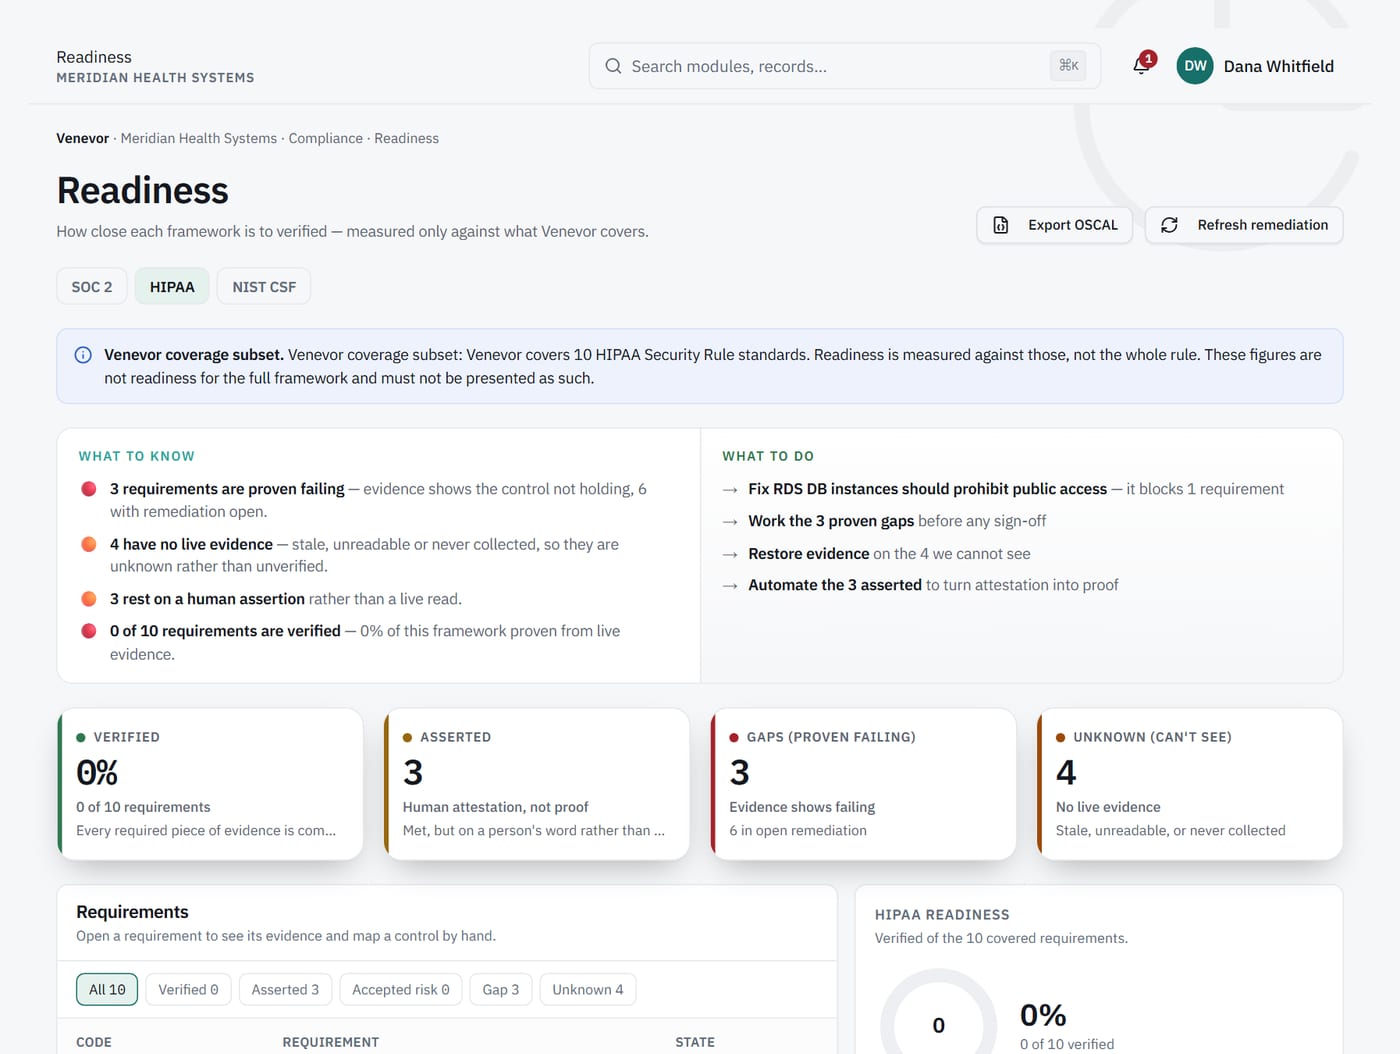
Requirements cover areas such as access control, audit and accountability, configuration management and incident response. Each one shows its readiness in five states, with verified and asserted kept apart.
What it does
Records each check result with its time and source, and never edits it afterward.
What it never does
Treat a check it could not read as a pass.
3Documentation
A starting point for your SSP and POA&M
FedRAMP SSP and POA&M foundation exports give your team a structured base for those documents. Assessment results also export in OSCAL format.
Capabilities
Built for NIST SP 800-171.
Rev. 2 and Rev. 3
Track the revision your contracts reference and plan for the other.
Shared with CMMC
One check counts toward NIST SP 800-171 and CMMC Level 2.
OSCAL import and export
Import OSCAL content and export assessment results in OSCAL format.
Evidence freshness
Each piece of evidence is marked fresh, stale or cannot verify.
Exceptions with expiry
Every exception has an owner and an expiry date, and it never overrides an automated status.
Assessor access
Assessors review controls and evidence, with export, and cannot change anything.
One set of evidence
The same checks count toward other frameworks.
- Government
CMMC
Prepare for CMMC Level 1, 2 or 3 assessments.
See CMMC → - Security
NIST CSF 2.0
Map your program to the six CSF 2.0 Functions.
See NIST CSF 2.0 → - Compliance
Compliance automation
Controls that prove themselves from live checks.
Learn more → - Compliance
Evidence
Every check result, timestamped and kept.
Learn more → - Compliance
Exceptions
Accepted gaps with an owner and an expiry date.
Learn more →
FAQ
NIST SP 800-171 questions.
Which revision should we use?
Use the revision your contracts and contracting officer specify. Venevor has packs for both, so you can track one and plan for the other.
How does NIST SP 800-171 relate to CMMC?
CMMC Level 2 aligns with NIST SP 800-171. Venevor maps each check to both, so evidence collected for one counts toward the other.
Does Venevor assess us?
No. Venevor helps you prepare by tracking requirements, collecting evidence and showing gaps. Your own team or an outside assessor makes the assessment.
Can we bring in our own control catalog?
Yes. Import a custom framework or OSCAL content, and map it to the same controls and checks.
See your NIST SP 800-171 readiness on real evidence.
A walkthrough built around your frameworks and the systems you already run.